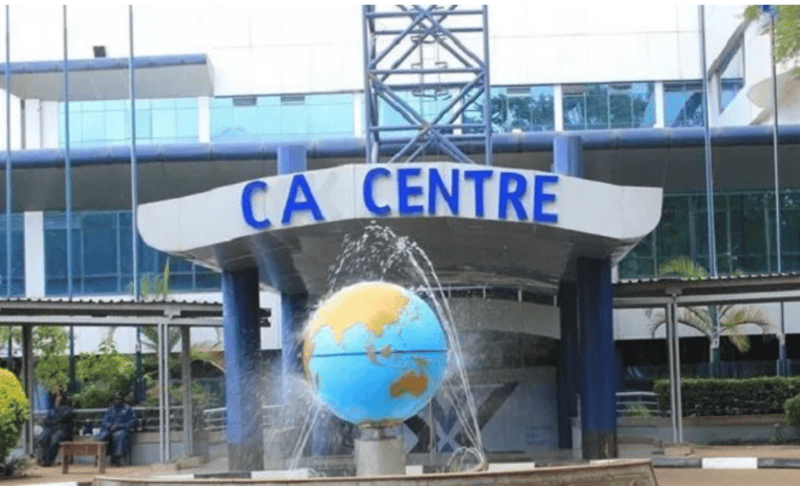
Kenya detected nearly 2.7 billion cyber threat events in three months, with attacks targeting web applications and attempts to crack passwords rising sharply, according to the Communications Authority.
Kenya’s digital systems faced a fresh wave of cyber threats between July and September, with detected activity rising by 14.45 per cent and attacks targeting web applications increasing by more than half.
The Communications Authority of Kenya (CA), in its latest quarterly cybersecurity report, recorded 2,696,335,021 cyber threat events during the period. That was an increase from about 2.36 billion in the April-to-June quarter.
The figures point to growing pressure on systems used by government agencies, businesses and service providers. However, they do not mean that billions of successful cyberattacks or data breaches occurred. The reported total measures detected threat events, which can include repeated or automated attempts against digital systems.
The latest figures also show that the risks are not limited to one type of attack. While system-related threats made up the overwhelming majority of detections, web application attacks and attempts to gain access by guessing passwords recorded notable increases.
Web attacks and password-guessing attempts surge
Web application attacks rose by 57.62 per cent to 27.4 million during the quarter, according to the CA report.
These attacks target weaknesses in websites and online applications. Depending on the vulnerability, criminals may attempt to access restricted information, interfere with services or gain unauthorised control of parts of a system.
Brute-force attacks, which involve repeatedly trying passwords or other login credentials, increased by 85.41 per cent to nearly 45 million. Such attempts can become more effective where organisations rely on weak passwords, leave remote-access services exposed or fail to introduce additional identity checks.
Malware-related threats also rose by 20.01 per cent to about 70.8 million. Malware is malicious software that can be used to steal information, disrupt systems or provide attackers with unauthorised access.
System attacks remained the largest category, accounting for approximately 2.55 billion events. The report attributed much of the activity to weaknesses in systems and networks, including software that had not been adequately updated.
CA Director-General David Mugonyi warned that weaknesses in digital infrastructure could threaten essential services and interrupt business operations.
“The exploitation of system vulnerabilities by threat actors continued to pose considerable threats to the delivery of critical services and the continuity of business operations,” Mugonyi said in the report.
The figures underline why cyber security is not only an issue for technology companies. Government portals, financial services, telecommunications networks and businesses that depend on online platforms can all be affected when their systems are exposed.
Why fewer advisories do not mean fewer threats
The National Kenya Computer Incident Response Team Coordination Centre (National KE-CIRT/CC), which operates under the CA, issued 20.26 million cyber threat advisories between July and September.
That was 2.36 per cent fewer than the advisories issued in the previous quarter, even as detected threat events increased.
The two figures measure different things. A detected event is activity flagged by monitoring systems, while an advisory communicates a warning or technical guidance to help organisations respond to a threat.
A decline in advisories therefore does not, on its own, show that Kenya’s cyber security has improved or that fewer threats required attention. The published figures do not provide enough detail to establish why the advisory total fell while detected events rose.
National KE-CIRT/CC coordinates cyber incident response and issues technical guidance to organisations and other stakeholders. Its work includes helping to identify threats, alert affected parties and improve the security of digital systems.
AI adds to the challenge
The CA attributed the rise in cyber threats to several factors, including delayed software updates, limited public awareness of phishing and other social engineering tactics, and criminals’ growing use of artificial intelligence.
Phishing involves tricking people into revealing information such as passwords or financial details, often through messages that appear to come from trusted organisations. Social engineering uses deception to persuade people to take actions that compromise their security.
Artificial intelligence can help criminals produce more convincing messages or scale up certain activities. But the report’s findings do not mean that every detected threat was AI-generated.
For organisations, the challenge is to address weaknesses in both technology and human behaviour. Even well-secured systems can be exposed when staff are deceived into sharing credentials or opening malicious links.
What organisations and users can do
The CA has urged organisations to update operating systems, applications and firmware promptly, use multi-factor authentication, strengthen password controls and ensure that firewalls and antivirus tools are properly configured.
Multi-factor authentication adds a second verification step beyond a password, making it harder for someone to enter an account using stolen credentials alone.
Individuals can also reduce their exposure by avoiding suspicious links, checking the sender of unexpected messages and never sharing one-time passwords or login details with callers claiming to represent a bank, mobile service provider or government agency.
Organisations should also have clear procedures for reporting suspicious activity and responding to incidents. Detecting a threat is only part of the response; the speed and quality of the follow-up can determine whether a weakness becomes a serious breach.
Kenya’s latest figures show the scale of suspicious activity being detected across its digital systems. The next challenge is to ensure that organisations can turn warnings into practical action, protect sensitive information and keep essential online services running.
You may also like
Category: Technology
Related Video: What Dangote’s proposed Lamu oil refinery could mean for East Africa
Related Explainer: Why the BCG Vaccine Leaves That Small Scar on Your Arm
About the Author
Maureen Onyango is a journalist passionate about storytelling, life coaching and spiritual lessons. She studied at the Kenya Institute of Management and enjoys telling stories that inform, inspire and empower communities.
 Facebook
 Twitter / X
 WhatsApp
 LinkedIn
 Telegram
 Reddit